The Monetary Authority of Singapore (MAS) opened a consultation on 6 November 2026 on a proposed Circular that would set supervisory expectations for every financial institution in Singapore to migrate to quantum-safe cryptography. The draft is not legally binding, but it gives dated milestones: a migration plan by 31 December 2027 for most firms, migration of critical systems by 31 December 2030, and migration of all remaining systems by 31 December 2034. Domestic systemically important banks, Critical Information Infrastructure Owners and NETS face earlier plan and critical-system deadlines. In RegMemo’s analysis, the Circular turns the February 2024 quantum advisory into a timed work programme that boards will have to resource and track.
Why MAS is putting dates on the calendar
The consultation paper, P019-2026, says there is no internationally agreed date for a cryptographically relevant quantum computer, but that such a machine could appear within the next few years and would break widely used asymmetric algorithms such as RSA and elliptic-curve cryptography. Those algorithms protect authentication, session establishment and digital signatures across banking systems, market infrastructure and customer channels.
The Circular builds on MAS’s February 2024 advisory on quantum cybersecurity risks. That advisory asked firms to assess exposure. The new draft goes further by telling firms what a migration plan must contain and by when critical systems should finish the move. MAS also points firms to the Cyber Security Agency of Singapore’s Quantum-Safe Handbook and Quantum Readiness Index for practical steps.
Comments close at 11.30 pm on 23 November 2026. Submissions will be published and attributed unless respondents ask for confidentiality.
What every financial institution would have to do
The draft sets five groups of expectations.
First, governance. Quantum-safe migration should have board or senior management commitment, clear ownership, enough budget and regular progress reports. Quantum risk should sit inside existing risk management, policy and procurement processes.
Second, a cryptographic asset inventory. Firms should list algorithms, bit lengths and protocols in use, the systems they support and their dependencies. Priority goes to assets that are critical to operations, internet-facing or tied to data with long retention periods.
Third, a risk-based migration plan approved by the board or senior management. The plan must cover the inventory and prioritised approach, quantum risk in enterprise risk management and procurement (including a rule that new systems support quantum-safe algorithms or can be upgraded within the indicative timeframe), interim controls for assets that cannot yet move, capability gaps and vendor alignment with the firm’s own deadlines.
Fourth, implementation. Firms should test performance and interoperability before deployment, because quantum-safe algorithms often need larger keys and more compute. Migration should be phased. Systems that cannot move yet need documented interim controls and a written reason for deferral.
Fifth, progress tracking. Firms should set interim checkpoints and quantitative targets, and watch for vulnerabilities in the quantum-safe solutions they deploy.
Three public deadlines, plus earlier ones for systemic firms
For all financial institutions, the indicative timelines are:
- 31 December 2027: develop a quantum-safe migration plan.
- 31 December 2030: finish migrating critical systems. A critical system is one whose failure would cause significant disruption to operations or materially affect customer service, including time-critical transaction systems and systems that deliver core services to customers.
- 31 December 2034: finish migrating all remaining systems.
Where technical or operational obstacles block a deadline, firms should document the reason and apply interim controls. MAS says the timelines may change as the threat, standards and supervisory practice evolve.
For Critical Information Infrastructure Owners, Domestic Systemically Important Banks and NETS, two extra expectations apply. They should submit a migration plan to MAS by 30 June 2027. Critical Information Infrastructure Owners should complete migration of Critical Information Infrastructure systems by 31 December 2029, a year ahead of the general critical-system deadline.
That split changes the calendar for the largest banks and for payment infrastructure. The June 2027 submission date leaves about 19 months from the consultation’s opening for those firms to inventorise cryptography, choose vendors and get board approval. The December 2029 Critical Information Infrastructure deadline forces those owners to finish their most sensitive systems before the rest of the sector finishes its critical systems in 2030.
How this sits with other supervisors
Hong Kong’s Monetary Authority and the Hong Kong University of Science and Technology launched a post-quantum cryptography toolkit for banks on 2 November 2026, aimed at practical preparedness. The European Union’s Digital Operational Resilience Act already requires ICT risk management and testing, and national supervisors across Europe and North America have issued quantum readiness guidance without Singapore-style hard completion years. MAS is among the first major Asian financial supervisors to put public, multi-year migration dates into a draft Circular that covers the whole financial sector.
The Circular would sit alongside the MAS Notice on Technology Risk Management, the Cyber Hygiene Notice, the Technology Risk Management Guidelines and the Outsourcing Guidelines. Firms that already treat cryptography as a technology risk item will recognise the inventory and board-reporting language. What is new is the calendar and the explicit procurement rule for new systems.
What to watch
- 23 November 2026: consultation closes at 11.30 pm Singapore time.
- First half of 2027: final Circular expected after MAS reviews comments; DSIBs, Critical Information Infrastructure Owners and NETS face a 30 June 2027 plan-submission date.
- 31 December 2027: migration plans due for all other financial institutions.
- 31 December 2029: Critical Information Infrastructure systems due to finish migration for Critical Information Infrastructure Owners.
- 31 December 2030 and 31 December 2034: critical-system and remaining-system migration deadlines for the wider sector.
Primary sources
- Monetary Authority of Singapore, Consultation Paper on Quantum-Safe Migration Guidance and Timelines for the Financial Sector (P019-2026), 6 November 2026
- Monetary Authority of Singapore, Advisory on Addressing the Cybersecurity Risks Associated with Quantum, February 2024
Related: Korea orders cyber checks at 580 firms after 40 hacks and plans to scrap network separation
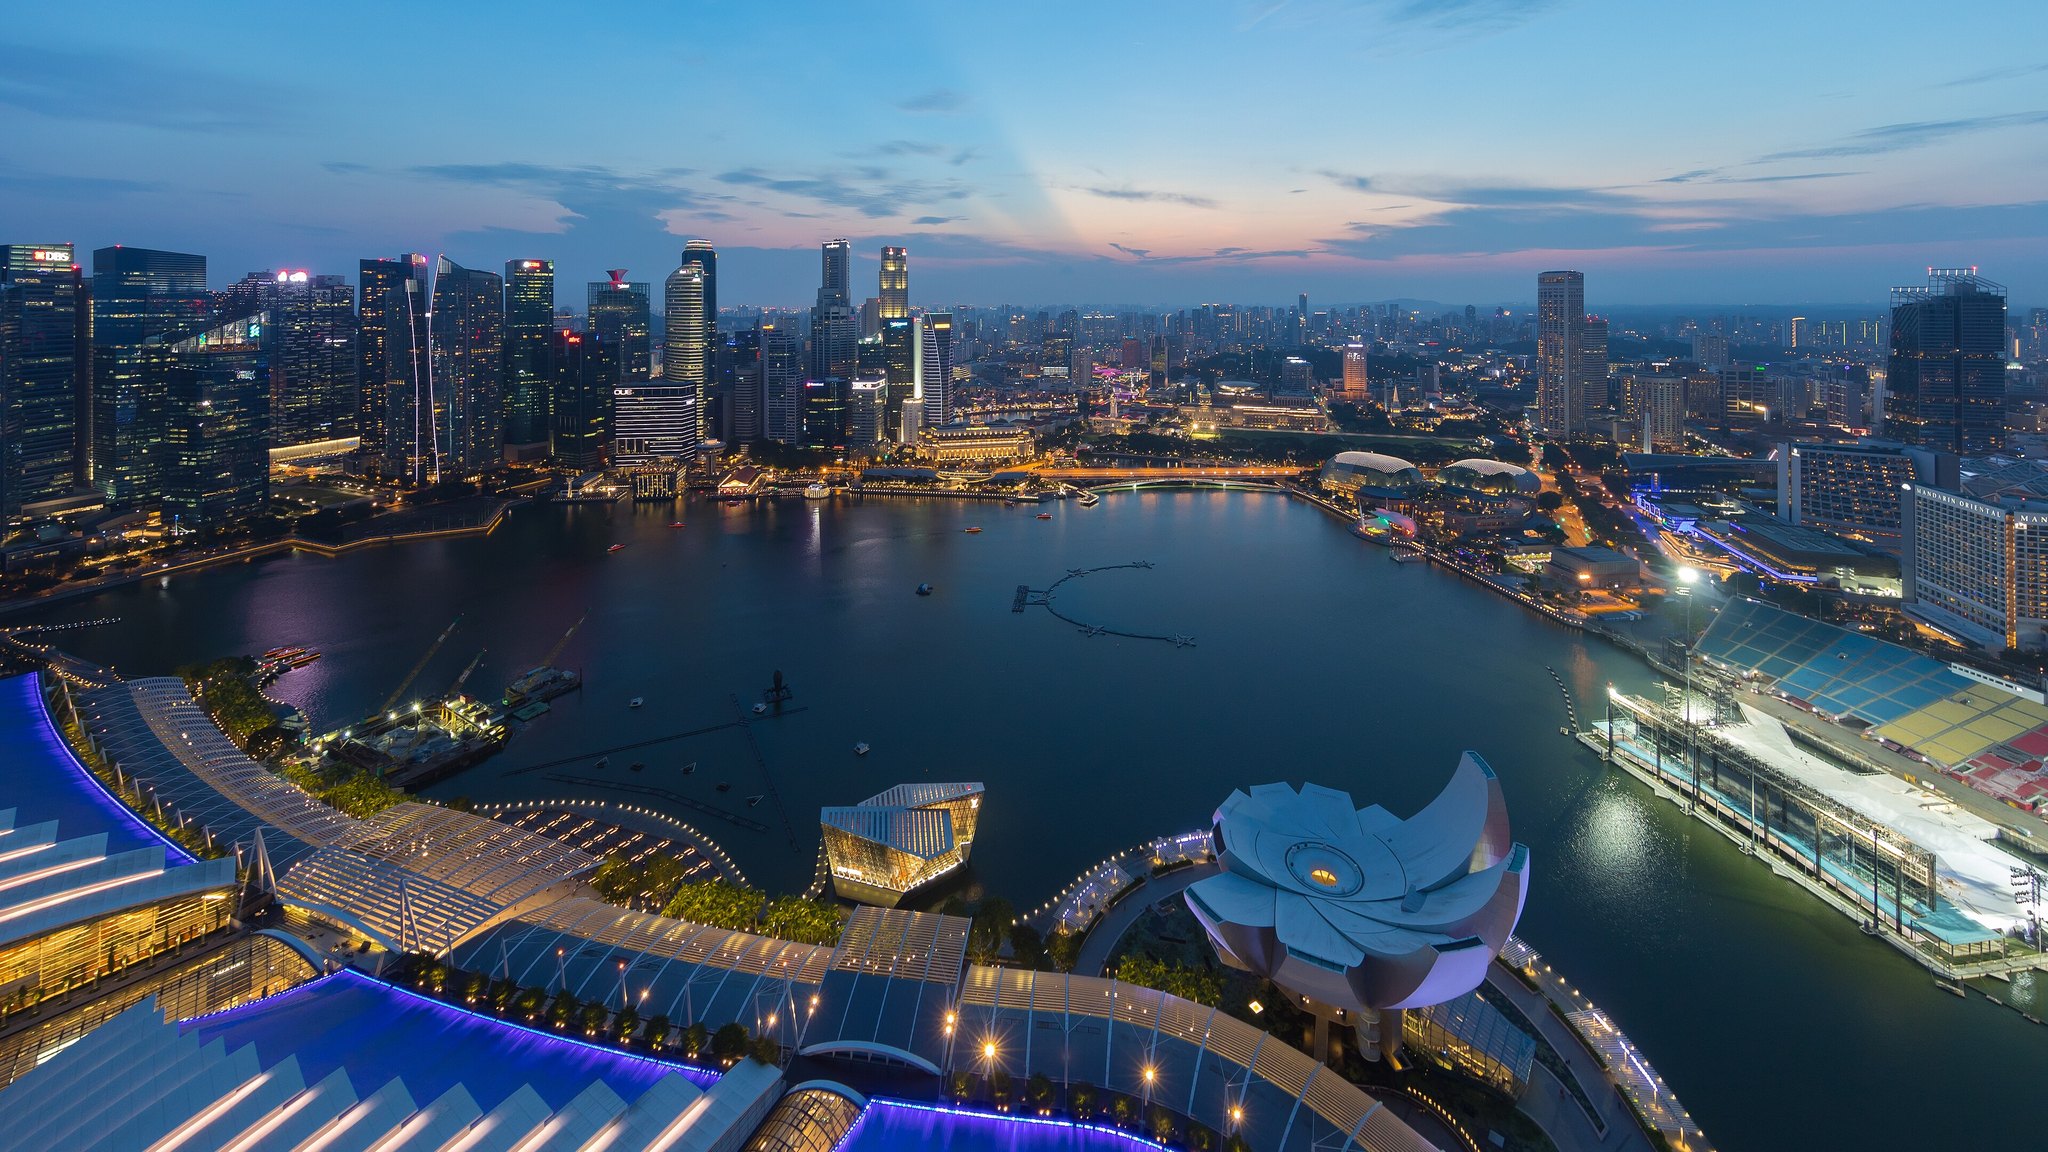
Photo (cropped): Basile Morin, CC BY-SA 4.0 via Wikimedia Commons
